In production, used by the firm's clients
Prime Accounts Inc
Prime Accounts Inc serves hundreds of clients from a PHP website that dates back to the early 2000s. I'm the firm's lead engineer and designer, and I plan the work directly with the owner. I built client accounts, invoicing, and a redesign in three languages, rebuilt sign-in, and secured every form. All of it runs on the original site, and sixteen regression suites test it on every change.
- Role
- Lead engineer and designer
- Built
- Redesign, sign-in, form protection, client accounts, and invoicing
- Today
- I maintain it and plan the work with the owner
- Proof
- Sixteen regression suites in CI
- Status
- Live at primestandard.ca, used by the firm's clients
- 1
Client sign in didn't work at all when I started. I rebuilt it in place, with invite-only accounts and safe password resets.
- 2
Become a client and every form under Forms used to carry its own copy of the same spam and forgery checks. They now share one version, and every form is tested against it.
- 3
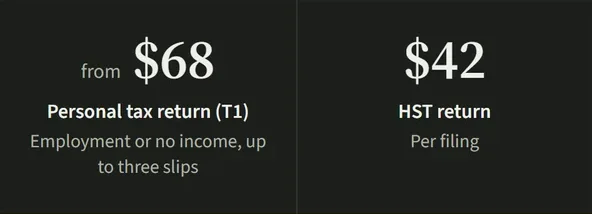
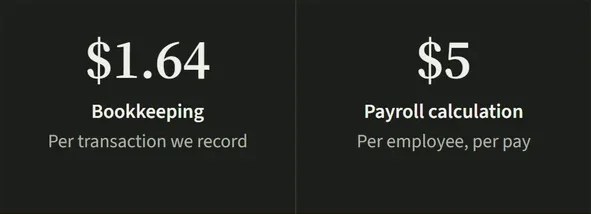
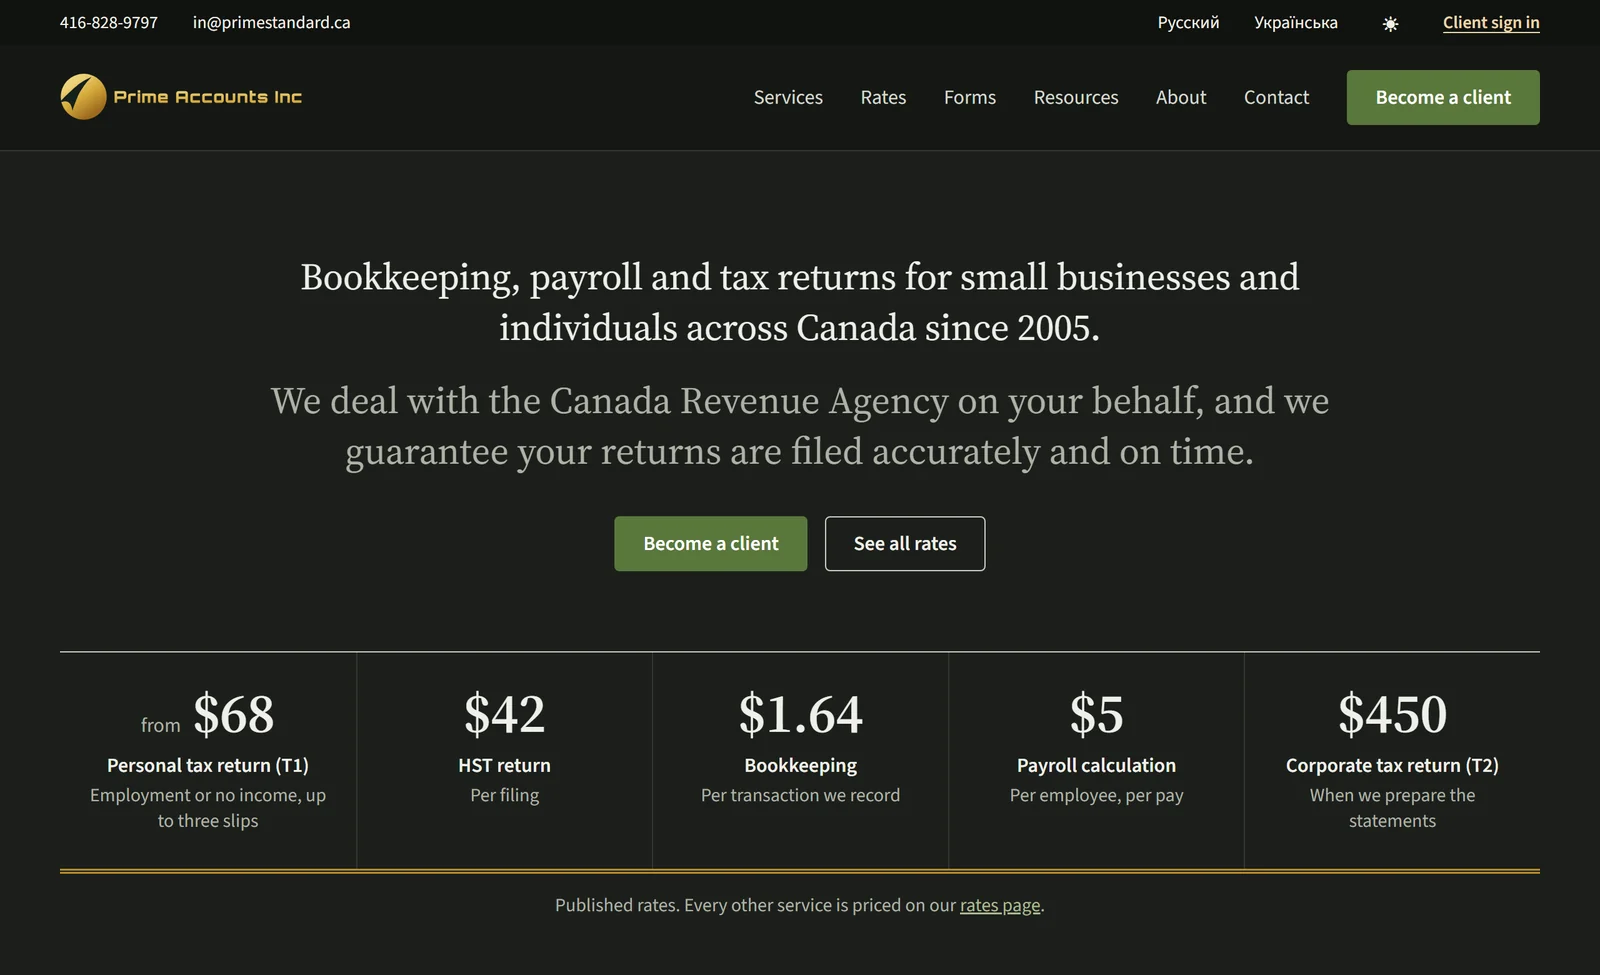
The rates were typed into each page by hand. They now come from one file the firm edits, so a price change shows up in all three languages at once.
Source: primestandard.ca
The problem
The site dates back to the early 2000s and still carried that era: a hand-built page for every language, prices typed into each one, and third-party tools nobody had touched in years.
Real clients still depended on its routes, forms, and email flows. Login was broken outright, the same spam and forgery checks had drifted apart across every form, and it handled data as sensitive as social insurance numbers.
I couldn't add a build step, bring in a framework, or rewrite the data layer, and every form had to keep working the way clients already used it.
What I built
The authentication system end to end: accounts, invite and password-reset links, and protection against repeated guessing. I moved every form's security checks into one shared library.
On top of the accounts I built the client side: income and receipts forms filed straight to the signed-in client, an invoice generator with a server-side tax engine and a PDF writer built from scratch, saved invoices with payments, and a home page showing HST due and the balance with the firm. I also redesigned the public site in English, Russian, and Ukrainian, with light and dark themes and layouts sized for phones.
Then I cleared out what the early-2000s site had left behind: abandoned third-party tools and stray server config files it no longer used. A test fails if any of them comes back.
I also fixed the smaller things a client expects in 2026. Every old .html address still lands on the right page with its details intact. Form email goes out through Microsoft 365, and an email that fails can be sent again instead of being lost. The tax guides were rewritten in English and Russian and checked against current CRA rules.
The hard parts
Authenticating people on a site with no working login and no framework.
Invite and reset links are built so the database never stores a secret that would work if it leaked, and repeated failed sign-ins are slowed down. A wrong password and an unknown address get the same answer, so the page never confirms who has an account.
Getting figures from a desktop database onto the web.
The firm keeps each client's HST due and balance in a desktop Access database. I wrote a module inside it that sends one client's figures to the portal with one click, where the client sees them after signing in. The office's access is limited to exactly that job, and the website only reads the figures.
Charging the right tax on every invoice.
GST/HST follows the buyer: the client's province for services, the delivery province for goods. Rates come from a dated rules file checked against CRA guidance, so a rate change is an edit to that file, not to the code. Provinces with their own sales tax get 5% GST and a warning rather than a guessed rate, and an invoice saved twice by mistake is flagged, while a corrected version saves normally.
Protecting social insurance numbers.
Social insurance numbers are validated before they are accepted and masked wherever staff see them. A refused form comes back with the client's answers, but the copy lives only in that browser tab and expires after a few hours, so nothing waits on a shared office computer for the next person.
The result
The firm's clients now get what they expect from a website in 2026: accounts, invoices, three languages, and a layout that works on a phone, all on the original PHP.
Forged and automated submissions stop at the form, and sign-in never reveals who has an account. Clients sign in to file their records and keep their invoices.
Built with
PHP, PDO, Microsoft Graph, and GitHub Actions, with sixteen dependency-free test suites in PHP and Node.
Every form checked the same way.
The same spam and forgery checks had been copied into every form handler, drifted apart, and never been tested. I moved them into one shared library, so a fix lands everywhere at once and every refusal is logged.
The tests submit every form against a throwaway database with email switched off, so each check is proven without sending a thing.
A forged or automated submission is turned away before any email goes out.
Next project
Meritory
The product I'm building now: a study tool for software engineering interviews, with accounts and a tested security protocol already in place.
Have somethingthat needs building?
If you have an idea you want built, or a project you'd like to talk through, I'd love to hear about it. I'm based in Toronto, and distance isn't a problem.